TL;DR: ISO 27001 and IASME Cyber Assurance are both robust frameworks for protecting data, but they suit organisations differently. ISO 27001 is an internationally recognised standard with up to 93 controls and annual audits; IASME Cyber Assurance is a UK-focused, often lower-cost route with 65 requirements, tailored guidance for organisations under 50 people, and an external audit every three years. This article compares the two across recognition, controls, cost, audits and prerequisites to help you choose the right standard.
Introduction
With cyber security threats constantly evolving, having measures to protect data is essential. Organisations often choose to implement IASME Cyber Assurance for comprehensive cyber resilience. Organisations also choose ISO 27001 as an effective way to protect data and apply an Information Security Management System (ISMS). So what are the differences between ISO 27001 and IASME Cyber Assurance, and why does that matter? In this article, we explore these differences to help organisations gain more clarity and support decision-making.
IASME Cyber Assurance Version 7
The latest version of IASME Cyber Assurance is aimed at making organisations more cyber resilient and references 65 security-related requirements. These requirements can be applied to organisations of all sizes, with specific tailored guidance for organisations with less than 50 people. There are two levels for the IASME Cyber Assurance scheme, with Level One being a verified self-assessment and Level Two being an audit. Successful applicants are awarded a 12-month certificate, with the Level Two audit being required every three years. Cyber Essentials is a valid prerequisite for IASME Cyber Assurance.
ISO 27001:2022
ISO 27001 is an international standard for information security management. It provides a framework for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS). The aim is to protect data and ensure confidentiality, integrity, and availability. The ISMS references the applicability of ISO 27002 in Annex A, which includes ninety-three controls, categorised into people, organisational, physical and technical controls. This standard can also be applied to organisations of all sizes.
Specific Controls and Themes
IASME Cyber Assurance has up to 14 themes and 65 security controls – it’s aimed at helping organisations be cyber resilient:
- Planning
- Organisation
- Assets
- Legal and Regulatory
- Risk
- Physical and Environmental
- People
- Policy
- Managing Access
- Technical Intrusion
- Change Management
- Secure Operations
- Resilience: Business Continuity, Incident Management, and Disaster Recovery
ISO 27001 is a structured framework of policies, procedures, and controls to manage information security risk – it contains ten clauses, of which six are mandatory (clauses 4 through 10):
- Scope
- Normative References
- Terms and Definitions
- Context of the Organisation
- Leadership
- Planning
- Support
- Operation
- Performance Evaluation
- Improvement
ISO 27001 refers to Annex A, which contains 93 security controls grouped into 4 themes:
- Organisational (37 requirements)
- People (8 requirements)
- Physical (14 requirements)
- Technological (34 requirements)
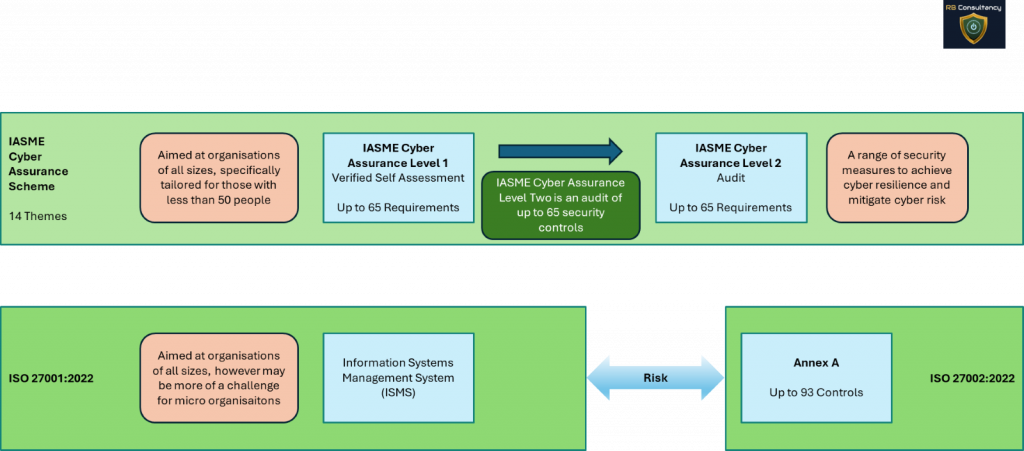
The diagram shows IASME Cyber Assurance and ISO 27001:2022, with key references to the number of requirements/controls and reference to Information Security Management System (ISMS)
Key Differences
- Recognition: ISO 27001 is an internationally recognised standard, whereas IASME Cyber Assurance is predominantly UK-based
- Controls (Measures): ISO 27001 has 10 clauses and up to 93 security controls, whereas IASME Cyber Assurance has 14 themes and up to 65 requirements
- Audits and Certification Cycle: ISO 27001 requires internal and external audits annually, whereas only IASME Cyber Assurance (Level Two) requires an external audit every three years
- Cost: Based on audit requirements alone, the cost of IASME Cyber Assurance can be a lot less than ISO 27001
- Prerequisites: There are no prerequisites for ISO27001, whereas IASME Cyber Assurance has Cyber Essentials (Level One) as a prerequisite
- Control Governance: ISO 27001 has a heavy focus on a risk-based approach for the implementation of security controls, whereas IASME Cyber Assurance can be considered as being more prescriptive (with mandatory requirements)
- Time to Achieve Certification: Typically, it can be quicker to achieve IASME Cyber Assurance than ISO 27001, based on the reduced requirement for testing and auditing alone
- Organisational size: IASME Cyber Assurance has specific (tailored) requirements for organisations of less than 50 people, whereas ISO 27001 does not
Mapping Exercise between IASME Cyber Assurance and ISO 27001
IASME carried out a mapping exercise in 2022 to guide how IASME Cyber Assurance maps to ISO 27001 – the results of the mapping show:
“IASME Cyber Assurance covers all the ISO 27001 requirements at an achieved or partially achieved level. IASME Cyber Assurance covers almost all the ISO 27001 controls explicitly or implicitly. Only 7 controls are not covered by any significant relationship with the IASME Cyber Assurance requirements – these largely relate to software development activities.”
The source document with full details can be downloaded from here
Where to Start
- ISO 27001 and IASME Cyber Assurance are both comprehensive
- Both can suit organisations in different ways
- Where to start can depend upon organisational size, security posture, IT setup and complexity
- We recommend a discovery call with RB Consultancy Ltd to help determine next steps
If you are also weighing up the certifications themselves, see our guide to the difference between Cyber Essentials, Cyber Essentials Plus and IASME Cyber Assurance
How RB Consultancy Ltd Help
- Holding CISSP and ISO 27001 lead implementer certification, we provide Consultancy for organisations to implement IASME Cyber Assurance and ISO 27001 (ISMS)
- As NCSC Cyber Advisor and Assured Service Provider, we advise organisations on how to implement the technical controls for Cyber Essentials and Cyber Essentials Plus
- As an IASME Assessor and Certification Body, we assess and certify organisations for Cyber Essentials, Cyber Essentials Plus, and IASME Cyber Assurance
Conclusion – key differences between ISO 27001 and Cyber Assurance
Both ISO 27001 and IASME Cyber Assurance offer robust frameworks for managing information security. While ISO 27001 is internationally recognised and comprehensive, IASME Cyber Assurance provides a more tailored approach for smaller organisations. Understanding the key differences, including cost, audit requirements, and control governance, can help organisations make informed decisions about which standard best suits their needs. Engaging with experts like RB Consultancy Ltd can further streamline the implementation and certification processes.
Written by Remo Belisari, Managing Director of RB Consultancy Ltd, an experienced cyber security professional and cyber advisor. Remo holds certifications relating to CISSP, ISSAP, ISO 27001, Cyber Essentials, IASME Cyber Assurance, and has many years experience in IT and cyber security. Remo has a history of supporting organisations from all over the world – including a Fortune 500 in USA and over 100 organisations across the UK. The views expressed in this blog are those of the author and do not necessarily reflect the views of RB Consultancy Ltd, its clients, partners, or affiliated organisations. The content is intended for general information only and should not be taken as legal advice.